Stepping back to the idea underneath the incidents.
Watch one request cross an API gateway and the whole trust problem is sitting right there.
Who’s asking. What proof of who they are came with it. What policy applies. What gets written down. What context survives the handoff to the next hop. A system that answers those out loud is doing trust work. A system that doesn’t is running on assumption, and assumption is where trust quietly rots.
Trust is not a vibe. It’s the policy you enforce and the evidence you keep at every point where control changes hands.
The pushback that lands hardest comes from teams with good observability. We’ve got traces, dashboards, a log pipeline. Isn’t that evidence? Not yet. A log line proves an action happened. It doesn’t prove the action was allowed. Telemetry turns into evidence the moment it ties back to the control that governed it, and not a moment before.
Policy without evidence is assertion. Evidence without policy is uninterpreted telemetry.
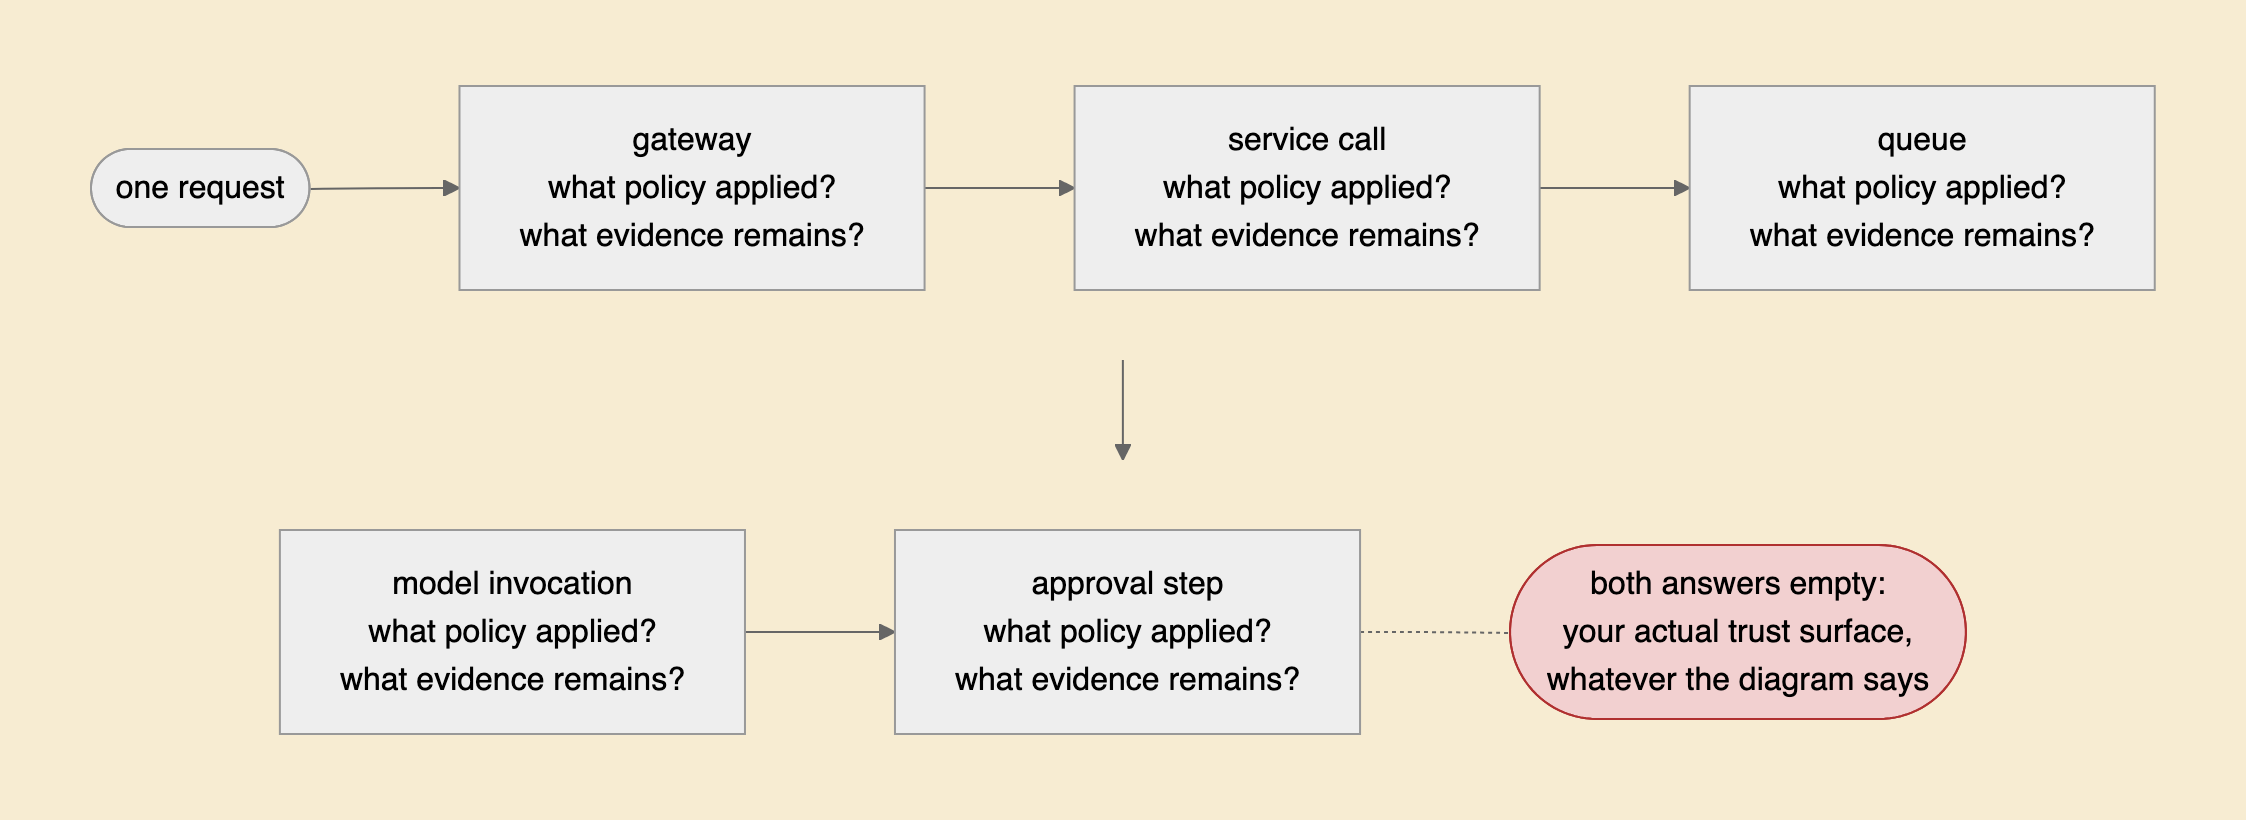
Try this: walk one request through your stack and list every place control changes hands. At each one, ask what policy applied and what evidence is left. Where both answers come back empty, that’s your real trust surface. Whatever the diagram says.